
Policy Management as a Service
Setting The Standard In IT Policy Excellence
The first step towards creating a secure computing environment is to develop IT policies and procedures that document the management and control of information.
To be successful, information systems security policies must be written using easy to understand language so that all parties understand the requirements and their obligations associated with the use of company information.
Five Common IT Policy Challenges
No one in-house has the subject matter expertise or experience in writing IT Policies
Existing policies are seldom reviewed to keep them up to date with changes in business and technology usage requirements
Writing and maintaining policy content in-house or on a bespoke basis is laborious and expensive
Stakeholder and user engagement requires a lot of management and effort
Monitoring and measuring user engagement with the content is difficult
Policy Management as a Service
Protocol Policy Systems have developed a suite of IT security policies, which are then uniquely tailored to align with your organisation’s practices.
Policy Management as a Service is a cloud-based subscription solution available in 3 versions – Lite, Essentials and Premium. The service allows an organisation to deliver up to date IT policies in under 5 weeks, eliminating the overhead of creating and maintaining those policies in-house.
All the hard work of gaining expert knowledge, developing, and maintaining policies to keep them current and mapped to standards such as ISO, PCI-DSS, and the ASD Essential Eight is taken care of by our experts on behalf of our customers.
Once in place, the policy management software makes the process of engaging and monitoring stakeholder and user interaction with the content both easy and visible.
What Does Policy Management As A Service Do?
Helps protect the assets of a business
Provides an organisation’s IT security framework
Provides a uniform level of control and guidelines for management
Improves security awareness using a messaging format that is easily available and understood
Reinforces team member responsibilities regarding the policies
Endorses the commitment of the CEO and senior management to protect valuable information assets and improve security posture
How The Policies Are Organised
Policy Management as a Service includes a comprehensive suite of policies covering key aspects of information system usage. All policies are written in plain English, with drop down explanations and links to relevant standards. The policies are set out by category for User, Manager, or Technical team members, which allows easy access to the policies that specifically relate to them.
The service also supports additional governance policy content, customers manage these documents in their unique instance of PMaaS and make use of many of its features and functions.
Compliance With Standards
Organisations adopt standards to help them optimise their business operations, manage risk, or comply with regulatory requirements. As an example, ISO 27002 is the code of practice for information security in many countries including Australia, New Zealand and the U.K. It sets the criteria for achieving best practice security management. Because all of the policy statements in Policy Management as a Service are mapped to international standards and best practice guidance, it provides evidence that security is being taken seriously by management, and stakeholders can have confidence that the organisation is acting responsibly.
User Engagement
Policy Management as a Service has been designed to address many of the shortcomings of in-house bespoke policy initiatives which may not address stakeholder and user engagement considerations. Examples of options the service provides include:
SAML integration with Azure AD or ADFS for single sign on
Stakeholder input regarding policy wording in the initial delivery phase and during any future review exercises
Present enrolled users with specific content from the overall policy framework to review
Invite third parties that are required to work with your systems and data to create a login and view the policy content
Review and accept policies onscreen – time efficient with no paperwork required
Create quizzes based on your unique policy content to test user comprehension
Generate user interaction reports
Get further detailed visibility through Insite Compliance reporting
Help users to develop and improve their understanding of the need for good security behaviours with our security awareness videos, topic index, glossary of terms and Top Tips page
Keeping Policies Up To Date
Under the Policy Management as a Service subscription plan all policy content is automatically kept up to date by us, as are the standards, mappings, and supporting material. Our subject matter experts are also available to adapt policies for customers as their business requirements change.
Frequently Asked Questions
If you’re thinking about Policy Management as a Service (PMaaS), you may have a few questions about how it works and what it can do for your organisation. Here are some of the questions we hear most often, with clear answers to help you understand the service.
Policy Management as a Service (PMaaS) is a cloud-based solution that makes the development, delivery and management of IT policies fast, easy, and efficient. It provides a suite of plain-English IT security policies, tailored to your organisation and maintained by policy experts as standards and best practices evolve. This removes the burden from in-house IT and GRC teams, promotes stronger security behaviour, and ensures policies remain current and relevant.
IT policies, or cyber security policies, are essential for protecting an organisation’s technology, data, and systems. They set clear rules for technology use, protect sensitive information, and reduce the risk of cyber threats and data breaches. Strong IT policies promote consistent cyber security practices among staff, support compliance with regulations and industry standards, and provide a framework for managing information security risks. Without them, organisations face increased security risks, operational disruption, and potential legal or reputational damage.
You’ll receive a branded suite of policies that are customised to your business requirements. The policies are written in plain English with explanation boxes for clarity. Additional features include:
- Mapped to recognised standards: examples being - ISO/IEC 27002, ISO/IEC 27017, PCI DSS, ASD Essential Eight
- User engagement tools: Online policy acceptances, policy review reminders, stakeholder mode
- User management: Usage reporting, enrolment for contractors and new-hires, user compliance tracking
- Content management: Policy review dates, policy visibility settings, DOCx export, online change requests
- Awareness resources: Quizzes, videos, security tips, glossary, topic index
Our library delivers content suitable for the general user population, Managers or Team Leaders, and Technical staff. The policy topics covered include acceptable use, access control, incident response, cloud security, mobile device usage, and remote access, to name a few. All policies can be customised to suit our clients business requirements.
Our policies are mapped or aligned to international standards and frameworks, including:
- ISO 27002, ISO 27017, ISO 22313, ISO 29151
- ISO 27001
- ASD Essential Eight
- PCI DSS
We continuously monitor changes to standards, regulations, and best practices. When something changes, we notify you of the details and provide options to apply revisions to your policy content. Ongoing we provide support to review and approve changes you wish to make to your policies as your business requirements change. This ensures your policy framework is always aligned with current cyber security best practices and compliance requirements without you having to track every change yourself.
Policies are written in plain English with explanation boxes to break down complex terms into everyday language. The software also includes a Glossary of Terms, Topic Index, quizzes, and awareness videos to improve comprehension. Engagement tools such as on-screen acknowledgement, reminders, and personalised dashboards help ensure employees not only read policies but also follow them in practice.
Organisations are typically up and running within 5 weeks – significantly faster than the 12–24 months often needed to write and implement policies in-house.
Demonstration Videos
IT Policy Challenges
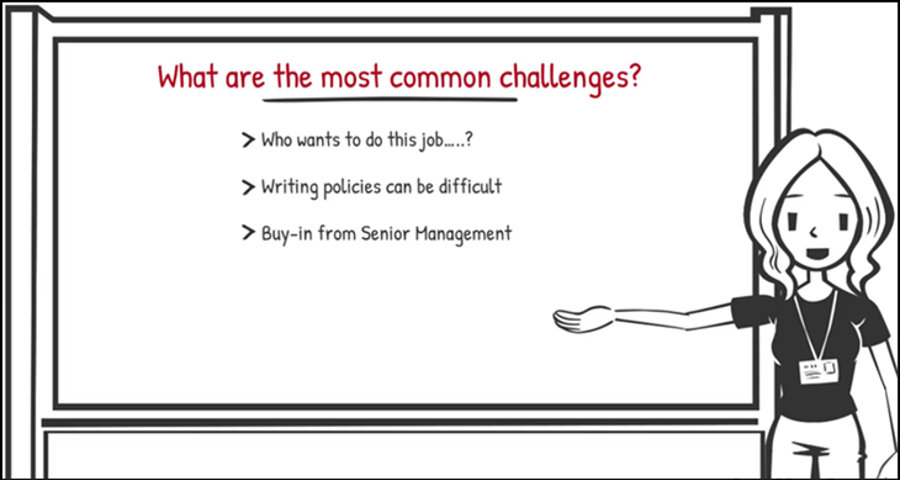
This video highlights the common challenges of developing, delivering, and maintaining IT Policies.
PMaaS in-depth
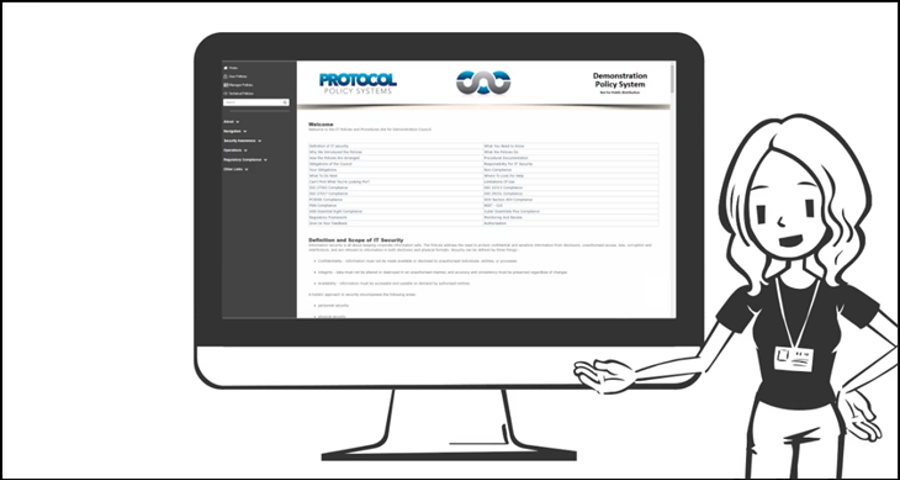
This video steps through the key aspects of the Policy Management as a Service offering.
Driving User Engagement
This video demonstrates how the Policy Management as a Service offering can help drive user engegement.
PMaaS Lite
This video steps through the key aspects of the IT Policy System (Lite)